Who killed the EV cert? A browser whodunit for Halloween.
Two companies called Stripe, a free certificate nonprofit, and the green badge that went missing.

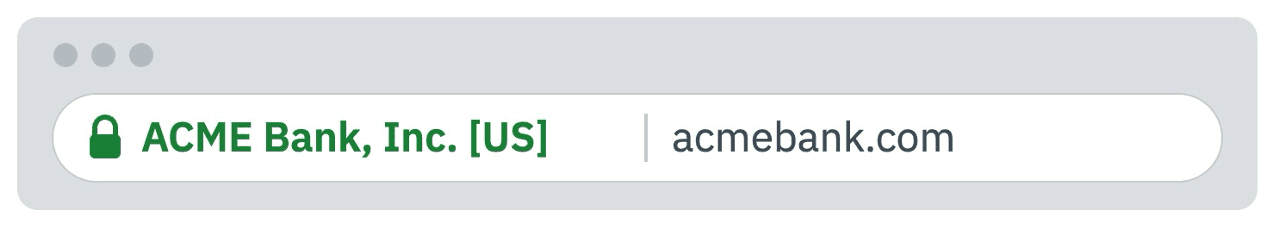
A decade ago, visiting a website could sometimes produce a cute little UI in the browser’s address bar: a green company name, reassuring typography, and a reassurance that a real company was responsible for the contents of the page.
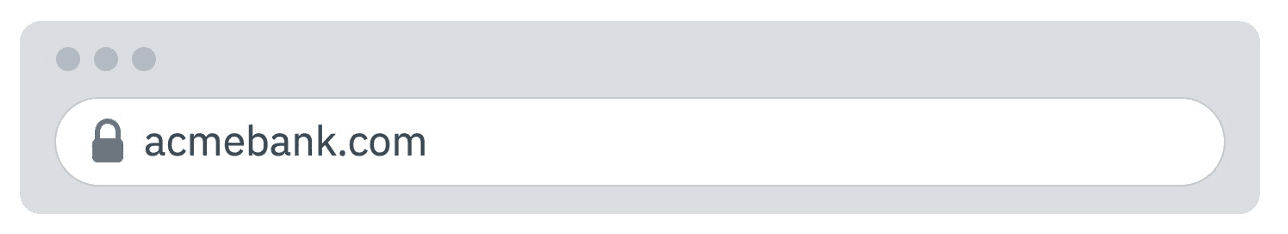
Today, that UI is gone, buried alive under several clicks, only for the weirdos who check website certificates.
With Halloween approaching, it seems worth reopening the case. Who killed the Extended Validation certificate’s starring role in the browser? The suspects include major browsers, fallible humans, a nonprofit with a noble security cause, and a Kentucky company called Stripe.
Like an Agatha Christie novel, several perpetrators played a role. And there was a silver lining: encrypted connections became nearly universal. Unfortunately, the end result was that verified business identity was severed from websites.
However, a new EU standard -- and the proliferation of AI agents -- may yet bring website identity back from the grave.
The victim had a promising career
Website certificates come with different levels of identity checking. Domain Validation, or DV, establishes control of a domain and is used for encryption. Organization Validation, or OV, added vetting on the organization behind it. Extended Validation, or EV, required a more detailed process for verifying the legal entity. The EV framework includes information such as incorporation jurisdiction and registration number.
Browser designers made some of this information available to human users. EV got the prime real estate: in browsers such as Chrome and Firefox, a company name appeared beside the address, often in green. The deal was that a business could pay for additional verification and receive an added presentation of trust to its website viewers.
The arrangement depended on those customers noticing the introduction. It turns out that humans are really bad at noticing trust indicators, or the lack thereof. So the utility of EV as a security measure never fulfilled its promise.
Case in point: when Chrome explained its decision to move EV information out of the address bar in Chrome 77, it cited research showing that changing or removing the indicator did little to change users’ security decisions. People would continue to enter sensitive information to fraudsters even when the company name was missing next to the URL.
The browsers were all on the same page. Safari had already reduced EV’s prominence in 2018. Firefox moved its indicator into the site-information panel in 2019.
The curious case of Stripe in Kentucky
It also became clear that the company name in the browser bar alone was not enough to establish trust. In 2017, security researcher Ian Carroll incorporated a company called Stripe, Inc. in Kentucky and obtained a completely legitimate EV certificate for it. The Stripe we are all familiar was incorporated in Delaware, so there was not a collision. But both companies were described by a browser as “Stripe, Inc.”
The demonstration prompted a public debate among browser-security specialists about accurate identity information that could nevertheless confuse users. A certificate could correctly identify Carroll’s company which, with the company name alone, inherited the reputation of an entirely different business.
EV certificates could carry details (like registration state) that distinguished the entities. But with limited UI in the browser bar, that additional information was discarded. Even so, few internet users could be expected to know the incorporation jurisdiction of every company they dealt with.
Kentucky Stripe was one of the nails in the coffin. Mozilla later cited this kind of name collision among its reasons for burying the indicator in clickthroughs.
The nonprofit with the free certificates
Meanwhile, the new service Let’s Encrypt from the nonprofit Internet Security Research Group (ISRG) was fixing an enormous security problem with the web. Let’s Encrypt made basic DV certificates free for any website. Its automated renewal made HTTPS practical for website owners who had resisted the pain of SSL: fees, manual configuration, and recurring maintenance.
It worked. Let’s Encrypt’s tenth-anniversary account describes global HTTPS usage in its Firefox-based measurements rising from below 30% to around 80% over roughly five years. Browser changes and hosting providers helped drive that progress, too.
Let’s Encrypt did not, and do not, issue OV or EV certificates. But that posed no real concern, since once browsers removed the prominent EV badge, the utility of the paid certificate and additional vetting was basically nil.
This crushed the commercial CA industry, for which paid SSL certs were its bread and butter. EV and OV certs still remain on sale, for niche buyers who have particular identity, procurement, or service requirements. But the idea of paying extra to reassure ordinary visitors was effectively dead.
Everyone gets a lock
An authentic website and a phishing imitator can both obtain DV certificates from Let’s Encrypt and pass the same TLS checks. They both get the same lock icon in the browser bar, because even a fraudster will take excellent care of your credit card information data in transit, and prevent man-in-the-middle attacks.
Let’s Encrypt explained this limitation before launching its public service. It expressed the view that a CA’s responsibility begins at encryption and ends at content, and that determining legitimacy is the job of others.
The utility of the lock icon was also questionable. In its 2023 explanation of the lock icon’s retirement, Chrome reported that only 11% of participants in a 2021 study understood its precise meaning. It also noted that nearly all phishing sites used HTTPS. Chrome replaced the address-bar lock with a settings-style icon; other browsers like Safari retain the lock.
But in 2026, we are still leaving internet users with the nagging question: who is responsible for a particular website?
A possible resurrection
The EU never let go of the idea that websites should have identity behind it. Their concept of Qualified Website Authentication Certificates – or “QWACs” -- provide a foundation for bringing verified business identity back into browsing. And as of January, 2027, browsers are required to support it.
Similar to an EV, QWAC carries verified identity information, but this time under the EU’s regulated trust ecosystem (instead of being left up to browser companies to decide.) But unlike EV, in the new so-called “2-QWAC” approach, that identity lives in a separate certificate, cryptographically linked to the website’s ordinary TLS certificate.
The beauty of this separation of concerns is that site can keep its existing HTTPS setup, including a free Let’s Encrypt certificate / subscription, and add identity alongside it as an optional add-on.
This architecture gives website owners a useful combination: free, automated connection security and independently checked business identity for users.
But what about the objection that humans don’t pay attention to these certs?
Well, in 2026, AI agents offer a very different audience for that identity information. While human attention is limited, software can programmatically check identity claims on every visit, examine the available attributes, and compare them to a known trust list. An LLM’s attention budget can accommodate more than a green label squeezed next to a URL.
Think back to the two Stripes. A personal AI agent could compare the certified entity’s jurisdiction in the QWAC certificate metadata with a trusted record of the intended merchant, then flag a mismatch to the human user.
The verification infrastructure will already be part of the browsing software as of January. An agent could then extract the identity data and use it when evaluating a transaction, and make it available to the person approving the purchase. That is not to say that identity will put a stop to internet fraud, but identity gives the agent currently missing piece of evidence to assess as part of a holistic website legitimacy evaluation, next to other signals like reputation / PageRank.
EV’s old bargain asked a distracted human to notice a small label and make a better decision. But in a world where AI agents, not humans, are the primary web browsers, the equation changes entirely. AI agents and 2-QWACs change the potential cost and value equation of publishing verified identity, and could give businesses a reason to invest in it again.
Website identity may yet rise from the grave.